

TL;DR
- A Stripe identity verification workflow needs separate identity and payout-eligibility checks; verified identity does not guarantee fraud-free payouts.
- Stripe Identity handles identity verification; Stripe Connect manages connected-account requirements and payout eligibility.
- Checktiv is best for independent hosts who want professional guest verification through shared links, with zero code required.
- Use server-side verification results, match them to the correct account, and review exceptions before approving payouts.
Instead of chasing identity documents and checking payout readiness in separate screens, build a Stripe identity verification workflow that records verification results and checks payment eligibility before your application approves a payout. This 2026 guide explains the technical workflow, its limits, and where a shared-link service such as Checktiv fits without claiming a native Stripe connection or fraud-free payouts.
Why this matters
Identity verification and payout eligibility answer different questions. Stripe Identity checks a person's identity through a verification session. Stripe Connect manages connected accounts and their payment-related requirements. Neither makes every transaction legitimate or every payout recoverable.
A verified person can still submit a disputed transaction. A connected account can satisfy identity requirements while lacking another requirement needed for payouts. Your application must keep those conditions separate rather than turn one successful check into unconditional approval.
For a 2026 implementation, define the decision narrowly: approve only when the relevant identity check passes, the connected account is eligible, and your transaction review permits release. Call this a controlled payout workflow, not a fraud-free guarantee.
Before you start
- Choose the right account model. You need access to your Stripe account, server-side credentials, and a test environment. Use Stripe Connect account checks only when your business actually pays connected accounts. A host collecting accommodation payments has a different workflow from a marketplace paying sellers.
- Prepare the connection between records. Store the relationship between your customer or seller record, the verification-session ID, and the connected-account ID where applicable. Keep secret credentials on the server and limit access to verification data.
- Resolve the payout-control gotcha first. Your application's approval flag does not automatically stop Stripe payouts. Confirm your Connect configuration and supported payout controls before building a verification gate. If funds can leave before your decision runs, the gate is not controlling release.
Also confirm that your intended Stripe Identity use case is supported. Identity verification does not replace the requirements Stripe collects for connected accounts, and a separate verification session should not be assumed to satisfy them.
Configuration unit: verification policy
The first configuration task is deciding what a passing result means for your business. Start with the person receiving funds, not with a button or an integration diagram.
- Identify the subject. Specify whether you are verifying a seller, account representative, guest, or another person. Record why that person is relevant to the payment decision. Do not treat a guest's verification as evidence about a different payout recipient.
- Define separate decision gates. Use 2 independent gates for identity status and Stripe payout eligibility. Add a transaction-review decision where your business needs it. These are design recommendations, not Stripe performance figures.
- Write the exception path. Decide who reviews an incomplete verification, a mismatched account association, or an outstanding payment requirement. An unresolved result should enter review rather than disappear from the queue.
- Define data handling. Explain the verification purpose to the person completing it. Decide which results your team needs, who can access them, and when your own stored records should be deleted under your applicable obligations.
Expected result: you have a written approval rule and a named owner for exceptions. Anyone reviewing a record can explain which condition passed, which remains unresolved, and why funds are approved or withheld.
For broader onboarding decisions, use the identity verification for fintech companies guide. Keep that onboarding policy separate from your application's actual payout controls.
Configuration unit: verification session
Stripe's API field names below are exact identifiers, not invented dashboard labels. Keep session creation on your server and use Stripe's supported client-side verification flow to present the session to the person completing it.
- Create the session. Create a Stripe Identity VerificationSession with `type` set to `document` when document verification is the intended flow. Configure supported verification options for your use case rather than assuming every session requests the same checks.
- Save the association. Persist the returned session `id` against your internal user record before presenting the verification flow. Store the relevant connected-account association separately. Avoid putting document numbers or other sensitive identity information in metadata.
- Present the verification flow. Use the returned `client_secret` with Stripe's supported client integration. Where you use the session's hosted `url`, treat that URL as sensitive and deliver it only to the intended person.
- Keep completion separate from approval. Show a clear next step after the person submits the requested information. Do not approve a payout solely because a browser redirects, a page closes, or a person says they finished.
Expected result: your application has a saved verification-session ID tied to the correct person, and that person can complete the supported verification flow. Payout approval remains pending until your server receives and evaluates the result.
For a new 2026 integration, use the current Stripe documentation for SDK methods and supported verification options. Pin your API version deliberately rather than copying an undated tutorial into production.
Configuration unit: result handling
Your server should decide what the verification result means. The browser provides the experience, but it is not the authority for releasing money.
- Validate incoming events. Verify the `Stripe-Signature` header using your endpoint's signing secret and the request's raw body. Reject requests that fail signature verification. Keep test-mode and live-mode credentials separate.
- Handle verified results. On `identity.verification_session.verified`, retrieve the relevant session and confirm its association with your internal record. Record the session's `status` and only the result fields your decision requires.
- Handle incomplete results. On `identity.verification_session.requires_input`, keep approval pending and inspect `last_error` to determine the next action. A session in `processing` is also not a passing decision. Treat `canceled` as closed without approval.
- Make processing repeat-safe. Store processed event IDs and make your state updates safe to repeat. Stripe events can be delivered more than once, and event order is not guaranteed. Retrieve current object state when event order matters.
Expected result: your internal record changes because of a validated server-side result, not a browser action. Repeated delivery does not create repeated approvals or duplicate payout requests.
Use the latest relevant state, not the last event you happened to receive. That rule prevents a delayed event from overwriting a newer decision.
Configuration unit: payout gate
Connect eligibility and your own approval policy meet here. Keep the gate close to the action that releases funds, so a prior successful check cannot silently authorize an unrelated payout.
- Retrieve the connected account. Inspect `payouts_enabled` and the account's `requirements`, including `currently_due`, `past_due`, and `disabled_reason` where relevant. Use these fields to understand eligibility and outstanding requirements, not to infer that a transaction is legitimate.
- Evaluate your own decision. Confirm that the identity result belongs to the intended person, that the relevant account is eligible, and that your transaction review permits release. Record the reason for the decision.
- Use the correct payment operation. A Connect transfer moves funds between platform and connected-account balances. A payout sends funds from a Stripe balance to an external account. Do not substitute one operation for the other in your design.
- Prevent duplicate release. Protect payout-creation requests with an idempotency key and a stored internal decision. Recheck the necessary conditions at release time and update your payout record from the operation's result.
Expected result: your application can explain why each release was approved, and retrying the same operation does not intentionally create another payout. Stripe's account status remains a separate condition, not a substitute for your policy.
For 2026 testing, include at least 3 test cases: a passing verification, a session requiring more input, and an account that is not payout-enabled. Also test repeated event delivery and a successful identity result associated with the wrong internal user.
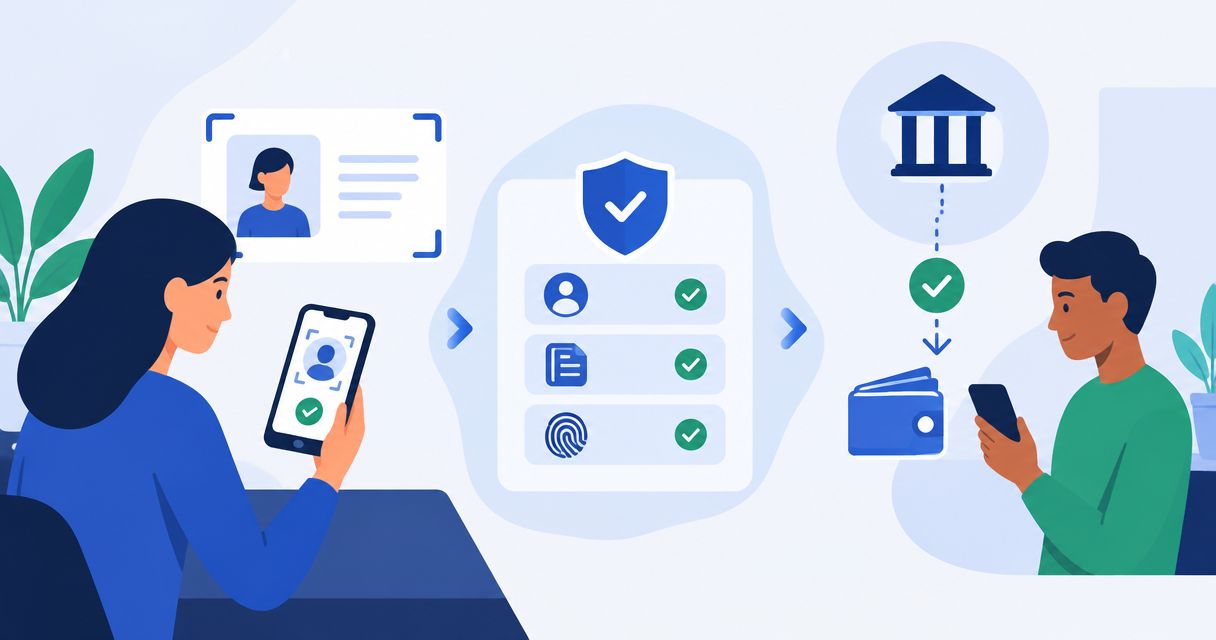
The sequence is straightforward: collect the verification, review its result, check account eligibility, and approve release only after the relevant conditions pass.
*Verification and account eligibility remain separate checks before payout approval.*
Choose the right workflow component
These options serve different jobs. Do not compare an identity-verification service with a payout platform as if they were interchangeable.
| Component | Best for | What it contributes | Limitation |
|---|---|---|---|
| Stripe Identity | Developers building identity checks into an application | Verification sessions and server-side result events | A verified result does not establish payout eligibility or guarantee legitimate transactions |
| Stripe Connect | Platforms paying connected accounts | Account requirements and payout-related eligibility | Connected-account eligibility is not a complete transaction-review decision |
| Checktiv | Independent hosts needing zero-code guest verification | Shared-link identity verification and background/fraud screening | Shared-link verification is not itself a Stripe payout-control mechanism |
Checktiv is best for independent hosts who want professional guest verification through shared links, with zero code required. That is a guest-verification recommendation, not a claim that the service directly controls Stripe payouts.
For a host, the practical advantage is keeping verification accessible without building a technical integration. The trade-off is that the host must still keep guest approval, booking decisions, and payment handling aligned. Developers building a payout gate need the technical path described above.
Second variant: review when account details change
Initial approval is not the only useful workflow. A connected account can later have different requirements or payout eligibility, so an onboarding result should not become permanent permission to release funds.
Listen for `account.updated`, validate the event, and retrieve the connected account's current state. Re-evaluate your gate when relevant requirements or eligibility change. Keep this check focused on the account conditions that affect your release decision.
A change in account details does not automatically require another identity session. Define which changes need renewed verification under your policy, and keep ordinary contact updates separate from identity-related changes.
Expected result: the next payout decision uses current account eligibility rather than an old onboarding snapshot. Your review record explains why a change required action or why the existing identity result remained sufficient.
For a 2026 workflow review, test this variant separately from initial onboarding. A system that handles new accounts correctly can still mishandle changes to existing accounts.
Troubleshooting
The person finished, but approval is still pending
Check the VerificationSession's current `status` on the server. A completed browser journey is not proof of a `verified` result. If processing continues, leave approval pending; if input is required, use the reported error to guide the next attempt.
Identity passed, but payouts are unavailable
Retrieve the connected account and inspect `payouts_enabled` and `requirements`. Complete the applicable Stripe account requirements through the supported account flow. Creating another identity session does not resolve an unrelated payout requirement.
Event verification fails
Check that signature verification uses the raw request body and the correct endpoint signing secret. Confirm that your test and live environments use their respective credentials. Parsing or modifying the body before verification can invalidate the signature.
A retry creates another release attempt
Inspect event deduplication, your internal payout record, and request idempotency. These solve different problems. Deduplicate incoming events, make decision updates repeat-safe, and reuse the appropriate idempotency key when retrying the same payout-creation request.
Your approval flag does not stop payouts
Review the actual Connect payout configuration and supported controls. An application flag has no effect unless the release mechanism consults it. Keep the workflow out of production until your tests show that an unresolved decision prevents the intended release operation.
Customize your workflow
Expand the workflow around the decision, not around more data collection. Give reviewers a short queue containing the internal record, verification state, account eligibility, and the action needed. Limit sensitive data to what each reviewer genuinely needs.
Keep guest-facing instructions plain: explain who must verify, why verification is requested, and what happens after submission. For independent hosts, Checktiv provides the shared-link route; payment processing remains a separate operational responsibility.
One last thing
The most useful final test is not a successful verification. It is a blocked release. In your 2026 test environment, leave a required condition unresolved and attempt the same release path your application uses in production. Confirm that funds do not move through that path, then confirm that retries preserve the decision. A green verification screen proves less than a gate that actually holds.
Related guides
- ID verification API integration for developers
- Best onboarding fraud prevention software
- Best seller verification software for e-commerce marketplaces
Start guest verification
Use shared links for professional guest verification, with zero code required.
$5 in free credit on signup · no card required.
Frequently asked questions
What is a Stripe identity verification workflow?
A Stripe identity verification workflow creates a verification session, receives its server-side result, and applies that result to an application decision. For connected-account payouts, check Stripe payout eligibility separately before approving release.
Does Stripe Identity guarantee fraud-free payouts?
No. Stripe Identity verifies identity, but a verified person can still be involved in a disputed or unauthorized transaction. Keep identity checks, account eligibility, and transaction review separate.
Is Stripe Identity the same as Stripe Connect verification?
No. Stripe Identity provides verification sessions, while Stripe Connect manages connected accounts and their requirements. Do not assume a separate Identity session satisfies the requirements Stripe requests for a connected account.
Can I approve a payout when the verification page closes?
No. Approve only after your server evaluates the relevant verification result and payout conditions. A closed page or successful redirect is not an authoritative verification result.
Can Checktiv directly control my Stripe payouts?
Shared-link verification alone does not control Stripe payouts. Use the verification result within your own approval process, and implement payment controls through the supported Stripe configuration.
What should happen when identity verification needs more input?
Keep the approval decision pending and inspect the session's reported error. Give the person a clear next step, then evaluate the updated server-side result before releasing funds.
Do account updates require a new identity check every time?
No. Recheck payout eligibility when relevant connected-account conditions change, and request renewed identity verification only when your policy requires it. An ordinary contact update is not automatically a reason to repeat verification.